Powered by Artificial Intelligence
Harness next-gen AI to analyze complex data, identify vulnerabilities, and prioritize risks—delivering faster, smarter protection.
Vines Sees What Hackers Hide. Unmask Hidden Threats with AI Precision.
Harness next-gen AI to analyze complex data, identify vulnerabilities, and prioritize risks—delivering faster, smarter protection.
Continuous monitoring with advanced ML detects and responds to attacks the instant they happen—always-on threat intelligence.
Aina, your AI security copilot, guides remediation step-by-step—making fixes simple, clear, and effective.
Pipe findings straight into your workflow—auto-create Jira issues, push alerts to Slack channels, and track fixes from detection to closure without context-switching.
Shift left with DevSecOps—run Vines in CI/CD to block risky builds, gate merges on severity policies, and emit audit-ready artifacts that keep releases fast and secure.
Automate at scale with REST APIs and webhooks—pull results, trigger rescans, sync dashboards, and integrate Vines data across your tooling with stable, versioned endpoints.
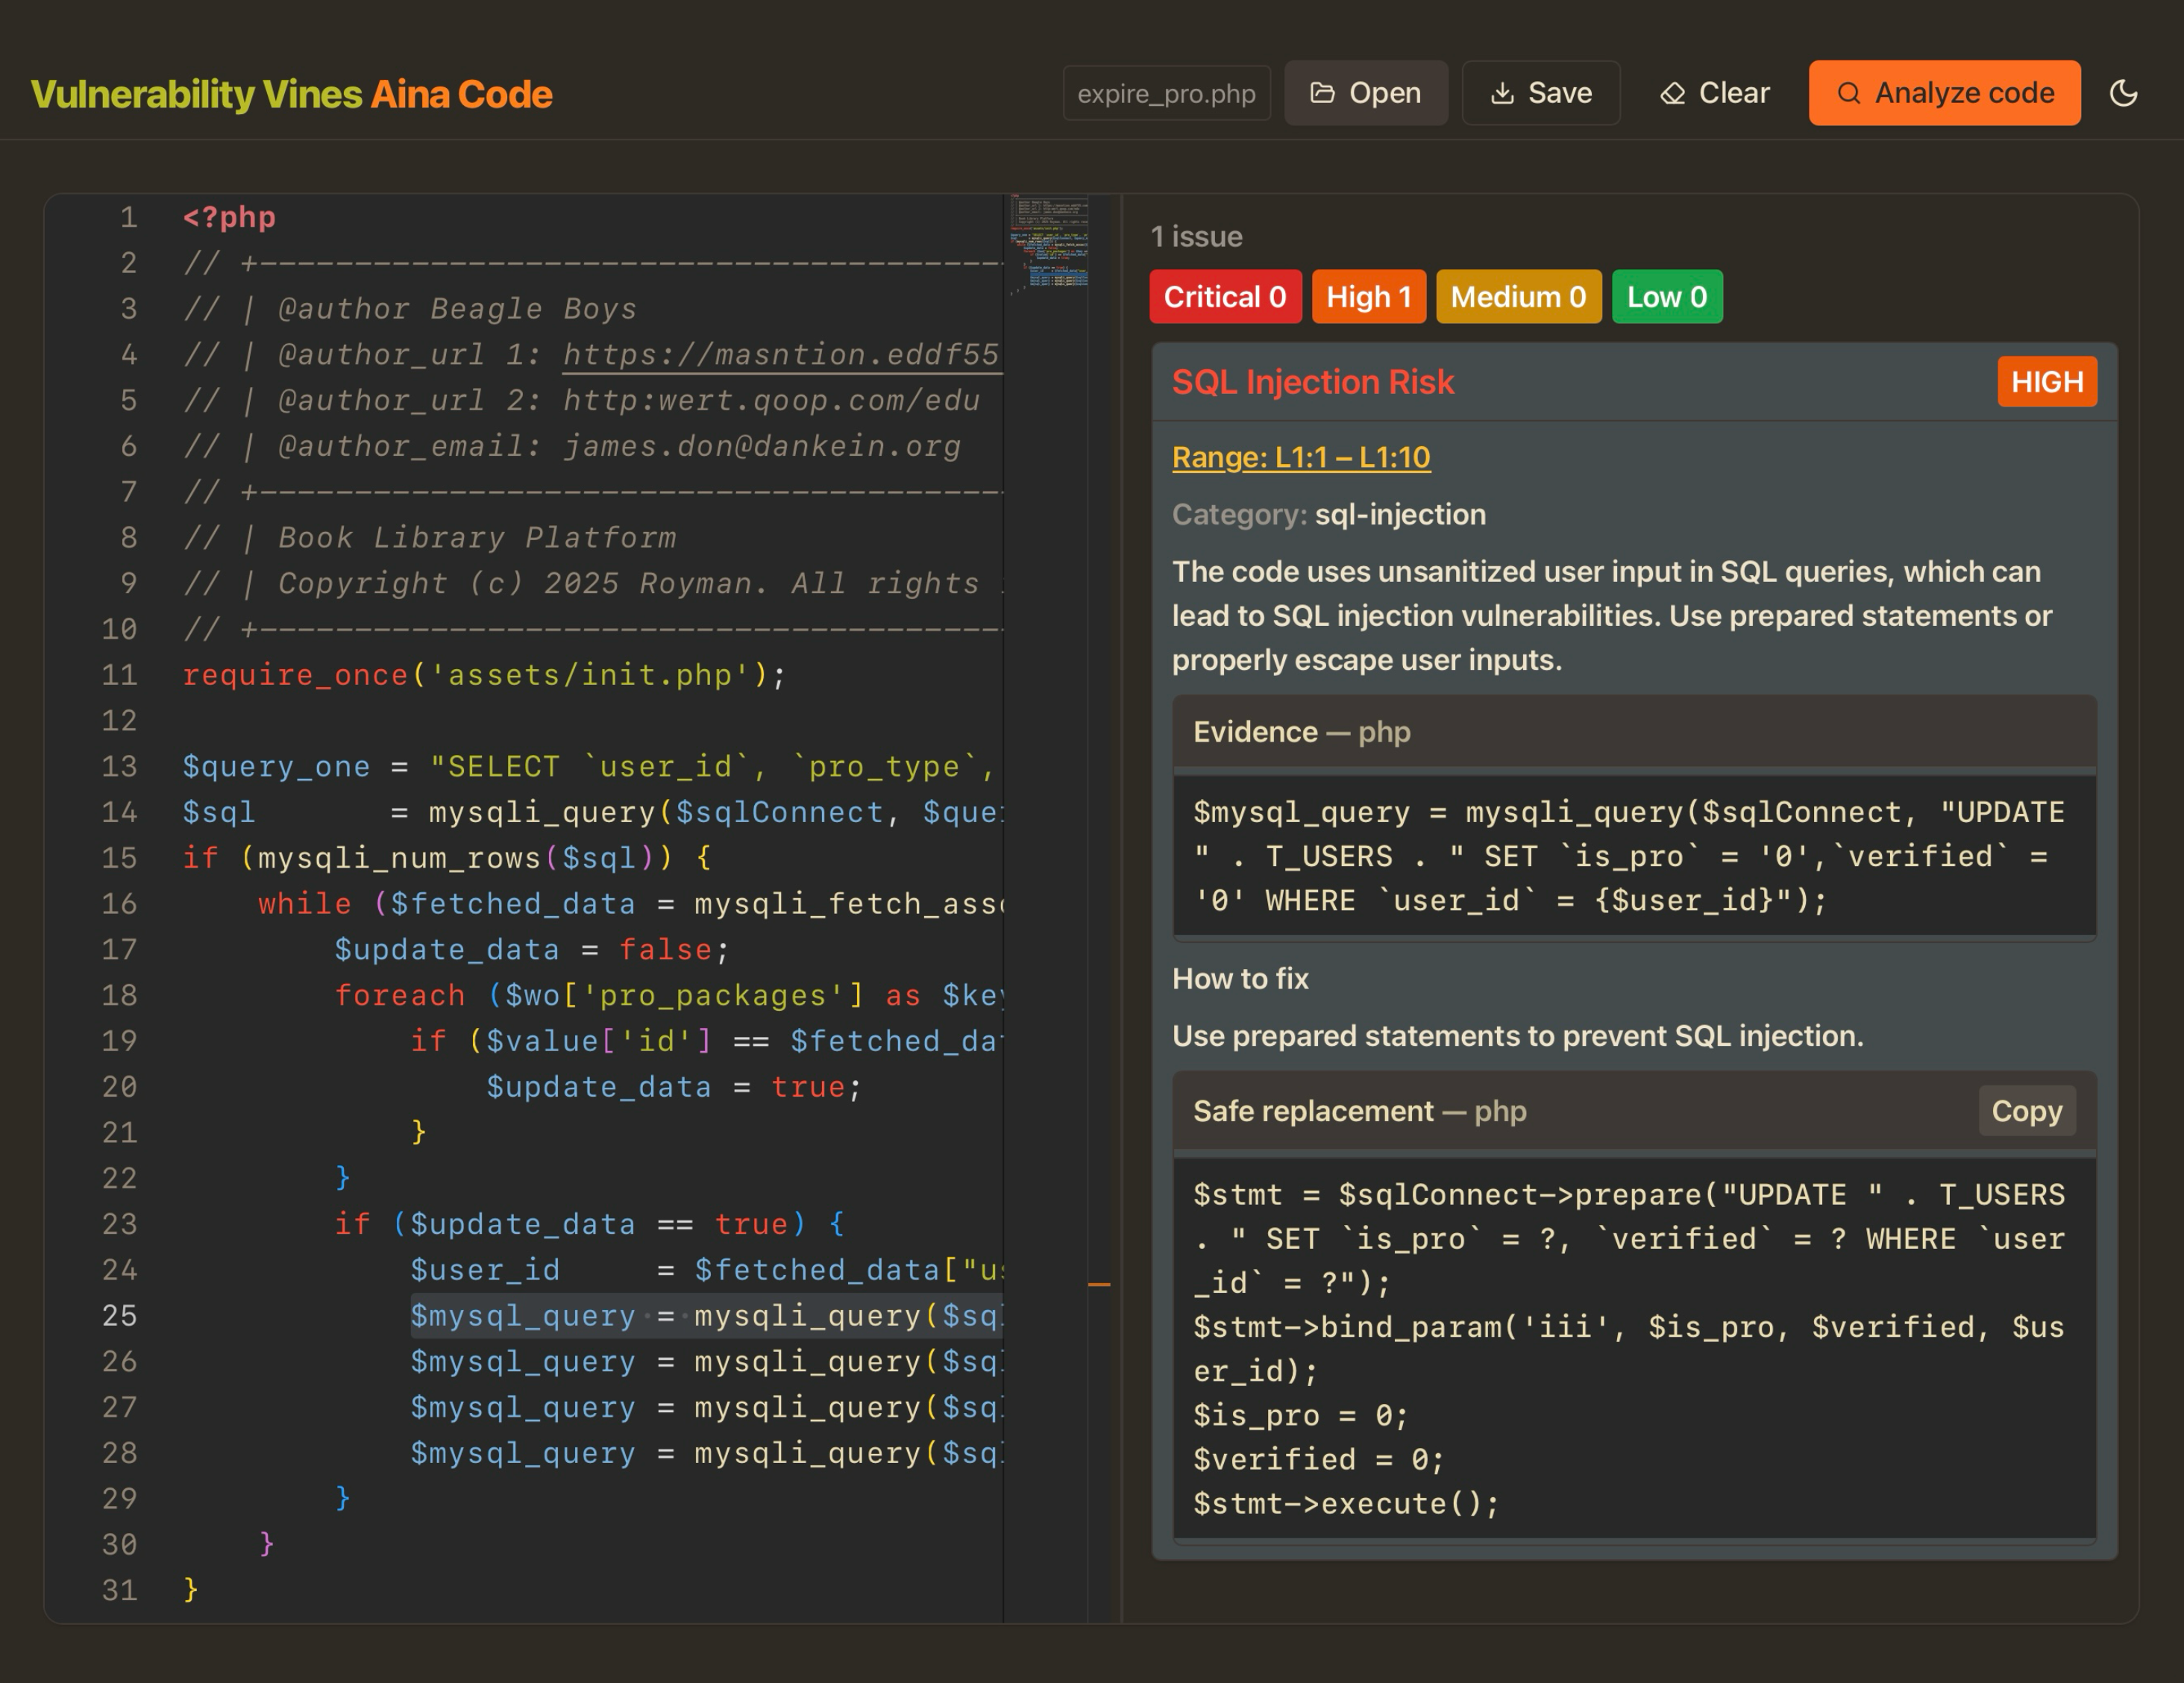
AinaCode analyzes every commit for insecure patterns, secrets, and misconfigurations—AI-assisted rules catch what linters miss and turn results into clear, fix-ready guidance.
RCCE professionals use Vulnerability Vines AI to secure your organization end-to-end. Across all 22 domains they examine each checklist line, interview and test, collect evidence, recommend fixes, implement, and verify— delivering an evidence pack + POA&M with owners and deadlines.